Agent Harness
Run Claude Code and Codex on your own machine under your organisation's policy: governed model requests and tools, one metered, sealed audit trail.
Nothing about the agent moves into the cloud. Claude Code, Codex and Cursor keep running on the developer's machine, with their own processes, files, built-in tools and agent loop. Sluis governs only what they send to external services: model requests and tool calls.
Region is not enforced for coding agentsA coding agent talks to your own provider subscription (Anthropic, OpenAI or Cursor), and the provider decides where that request is served. Sluis cannot pin the region, so on the agent plane residency is recorded, not enforced: a turn is never refused on jurisdiction, and its audit row records the region as unverified.
If residency must hold for every call, switch the coding-agent routes off in Compliance › Residency. They are then refused, and every refusal is audited.
The local client signs in to Sluis with an agent key and talks to the ingress its protocol speaks:
/agent/claudespeaks the Anthropic API, for Claude Code./agent/codex/v1speaks the OpenAI Responses API, for Codex./agent/cursorspeaks Cursor's Connect protocol over protobuf./agent/mcpis a stateless Streamable HTTP MCP endpoint that carries the governed tools.
These clients are examples, not an allow-list. Pi, T3 Code and any other client that accepts an Anthropic Messages, OpenAI Responses or MCP base URL and API key use the same Agent Harness.
Setup in four steps
Work through this page in order:
- Connect a subscription. Claude, Codex or Cursor, once per provider account.
- Create an agent key and link it to that account. A key spends only the accounts it is linked to, and its secret is shown once.
- Configure the local client. Keep the key in
SLUIS_AGENT_KEYand point the base URL at/agent/claudefor Claude Code,/agent/codex/v1for Codex or/agent/cursorfor Cursor. - Register the tool endpoint (optional). Governed tools arrive only over
/agent/mcp, registered separately: a base URL adds none.
Connect a subscription
Connect your Claude, Codex and Cursor subscriptions in the Console, under Gateway › Agent Harness › Connections. Claude connects with a setup token, Codex through OpenAI's device authorization and Cursor through a browser login. Sluis checks the credential with the provider before it stores anything.
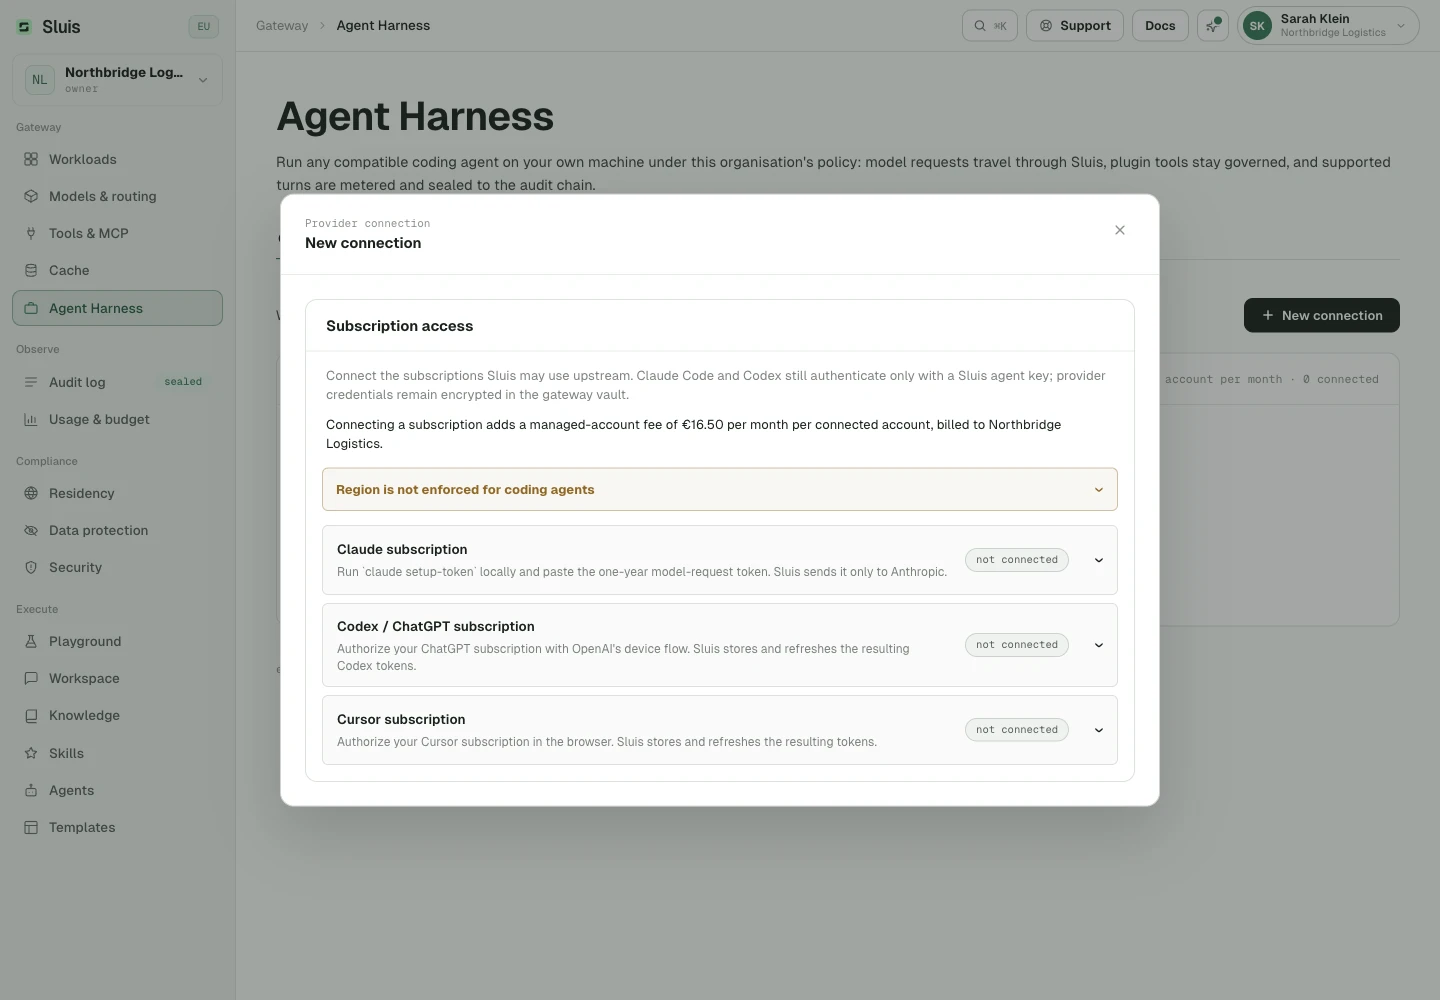
Claude: setup token
You need Claude Code installed on your machine and signed in to a Claude subscription that may make model requests.
- Run
claude setup-tokenin a terminal. It prints a long-lived token, good for about a year, that starts withsk-ant-oat. - In Gateway › Agent Harness › Connections, connect a Claude subscription and paste the token into the Claude field. The field is masked and autocomplete is off.
- Submit. Sluis verifies the token with Anthropic before it stores anything.
- A verified token is sealed into the gateway vault, encrypted. It is never shown again, never returned to a client and never sent anywhere but Anthropic.
If the token does not go through, nothing is stored and nothing is billed:
- Anthropic rejects the token: Sluis answers
422and creates no account. Runclaude setup-tokenagain and paste the newest token, because a new token retires the previous one. - Anthropic rate-limits the check (
503) or does not answer (502): the token is not at fault. Wait a moment and connect again.
Each member has one Claude account. Connecting again replaces its token instead of adding a second billable account.
Codex: device authorization
You need a ChatGPT plan that includes Codex.
- In Gateway › Agent Harness › Connections, start the Codex device login. Sluis asks OpenAI and shows you a verification URL and a user code.
- Open that URL with the button, sign in to OpenAI, enter the code and approve. OpenAI may ask for MFA.
- Keep this browser tab open while you approve. The Console keeps checking until OpenAI confirms.
- On approval Sluis stores the access and refresh tokens encrypted in the gateway vault and refreshes them for you.
Good to know:
- The exchange runs in this browser tab. Leaving the page, or switching to another tab of the view, stops the login, as Cancel device login does, and no account is created.
- Refresh-token rotation is serialized across replicas, so two gateway instances never rotate the same token at once.
- A user code expires. An expired flow reports
expiredand has to be started again. - An account whose stored credential OpenAI later rejects stops serving until a person reconnects it.
Cursor: browser login
- In Gateway › Agent Harness › Connections, start the Cursor login. Sluis opens a one-time Cursor sign-in session.
- Open the Cursor page, sign in and approve the CLI connection.
- Keep this tab open while Sluis waits for Cursor to confirm. Sluis then stores and refreshes the resulting tokens in the gateway vault.
A login that expires before Cursor confirms it creates no account. Start a new one.
Sluis encrypts these credentials, keeps them in the gateway vault and refreshes them there. A provider token never reaches the local client, the logs, the audit records or the traces. The clients only ever hold their Sluis agent key.
Who can connect, and what they see
- Connecting is self-service: a member can add their own subscription.
- Owners and admins see every account in the organisation. Members see only their own, and do not see the Agent keys and Plugins tabs.
- The Connections table credits usage to the provider that actually served each request, so a key linked to Claude and Codex never counts one call twice.
- Gauges show requests and tokens against the requests-per-minute (RPM) and tokens-per-minute (TPM) limits of the linked keys.
Create an agent key
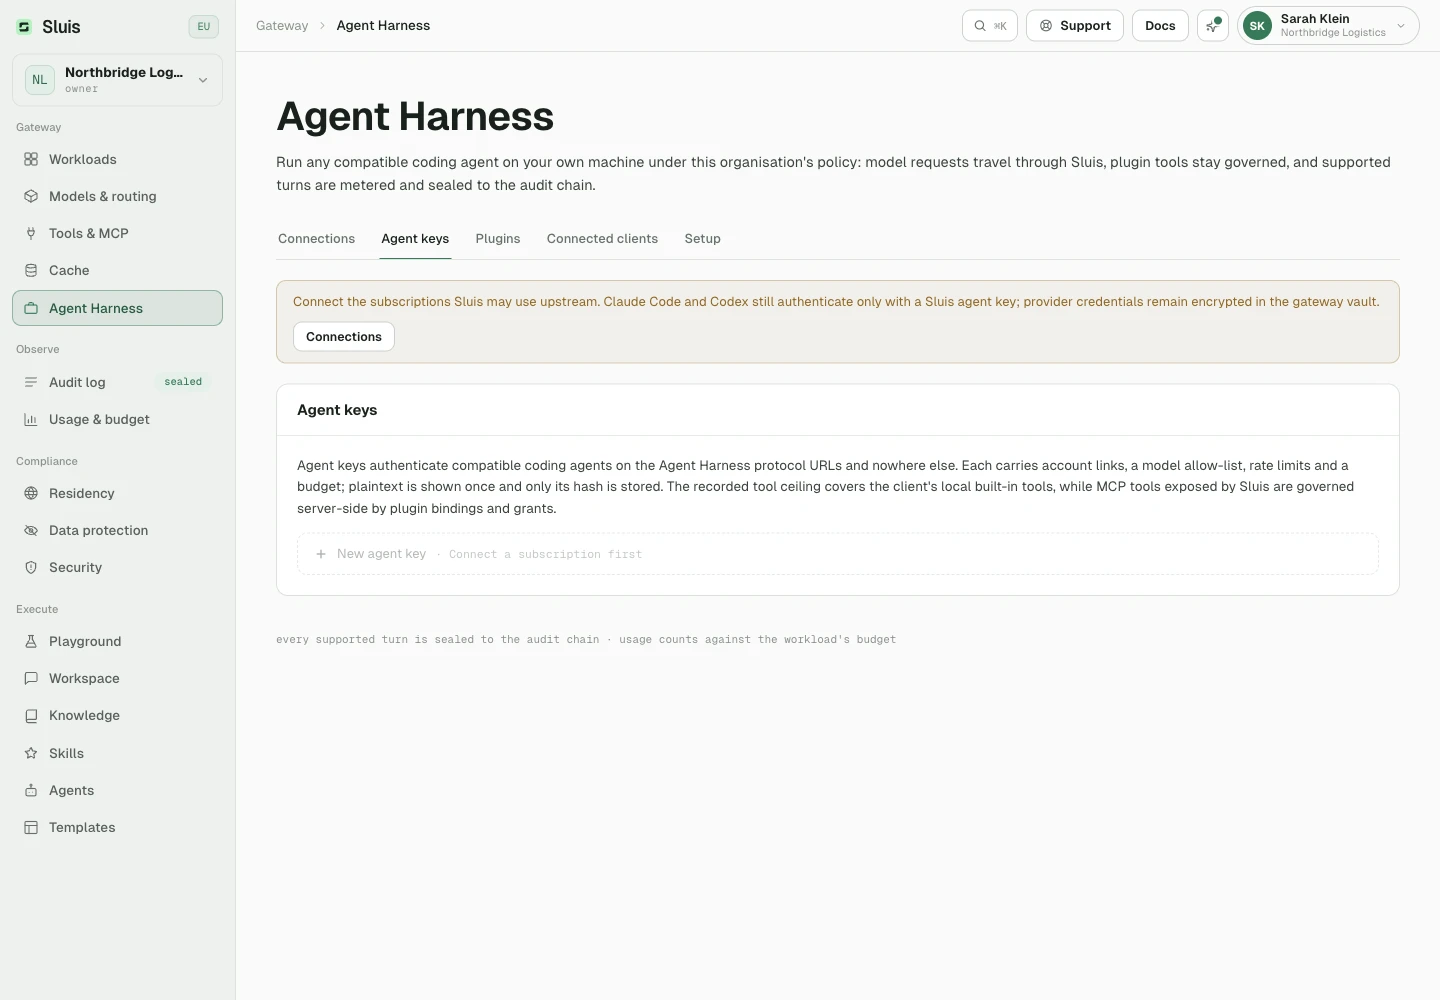
Create agent keys in Gateway › Agent Harness › Agent keys, separately from your API keys, because the two purposes are isolated.
One key, one purpose
- An agent key works only on
/agent/*. An ordinary API key works only on/v1/*. - An ordinary API key on
/agent/*gets a bare404, as if the route did not exist. On/agent/mcpit gets a401. - An agent key on
/v1/*gets a401, and so does an agent key sent in the wrong header (see Credential headers below). - No refusal says which purpose the key had.
Create a key
- Choose New agent key and give it a name.
- Link subscriptions from one searchable list of your active subscriptions. Link at least one account, and at most one per provider.
- Optionally limit the models. The searchable picker offers only models of the linked providers. Leave it empty to allow every model the selected subscriptions can serve.
- Copy the secret. It is shown once, and only its hash is stored.
Afterwards, from the key list:
- Edit changes policy and links without changing the installed key.
- Rotate & copy invalidates the old secret and shows one replacement once. Use it if the plaintext is lost.
- The Setup tab explains each client route.
Built-in tool ceiling
A key also records the organisation's ceiling on the local client's built-in tools, written in Claude Code's tool grammar (Tool or Tool(rule)) and checked when the key is created. The developer's client enforces that list on the machine. Sluis does not block built-in tool calls itself.
An empty list records no ceiling. Sluis reads the ceiling in one place only: to decide which tool names a skill may mention, so a skill can never widen a key (see Context and skills below).
The tools Sluis gates itself, on every request, are the MCP tools it exposes: see the plugins below.
Point the clients at Sluis
Claude Code
Claude Code needs one base URL and one credential. Set ANTHROPIC_BASE_URL to this gateway's Claude ingress, and ANTHROPIC_API_KEY to the agent key you keep in SLUIS_AGENT_KEY.
A base URL adds no tools: the Anthropic protocol has no plugin discovery. Register the MCP endpoint yourself, with claude mcp add or a .mcp.json entry. Both reference ${SLUIS_AGENT_KEY} instead of the key, so no secret lands in a committed file.
Codex
Codex reads its provider block from ~/.codex/config.toml:
- Point
base_urlat the Responses ingress,/agent/codex/v1. - Set
wire_api = "responses"andenv_key = "SLUIS_AGENT_KEY". - Add the same MCP endpoint under
[mcp_servers.sluis].
Copy-paste setup
The tabs below cover both clients. The Console generates the same blocks with your gateway's public URL already filled in, in Gateway › Agent Harness › Setup.
# the agent key is shown once, at creation: keep it in the environment
export SLUIS_AGENT_KEY='sluis-9f2c…'
export ANTHROPIC_BASE_URL='https://api.sluis.ai/agent/claude'
export ANTHROPIC_API_KEY="$SLUIS_AGENT_KEY"
# a base URL adds no tools: register the MCP endpoint separately
claude mcp add --transport http sluis 'https://api.sluis.ai/agent/mcp' \
  --header 'Authorization: Bearer ${SLUIS_AGENT_KEY}'
// .mcp.json: the same registration, kept with the project
{
  "mcpServers": {
    "sluis": {
      "type": "http",
      "url": "https://api.sluis.ai/agent/mcp",
      "headers": {
        "Authorization": "Bearer ${SLUIS_AGENT_KEY}"
      }
    }
  }
}
# Codex reads the key from SLUIS_AGENT_KEY, never from the config file
codex exec -m openai/gpt-5.4 'tighten the retry test'
# ~/.codex/config.toml
model = "openai/gpt-5.4"
model_provider = "sluis"

[model_providers.sluis]
name = "Sluis"
base_url = "https://api.sluis.ai/agent/codex/v1"
env_key = "SLUIS_AGENT_KEY"
wire_api = "responses"

[mcp_servers.sluis]
url = "https://api.sluis.ai/agent/mcp"
bearer_token_env_var = "SLUIS_AGENT_KEY"
default_tools_approval_mode = "approve"
Cursor
Set Cursor's base URL to this gateway's Cursor ingress, /agent/cursor, with the agent key in the Authorization header. A client that cannot set a base URL may point at the bare origin instead, because Cursor's protocol pins an absolute path.
The documented route is POST /agent/cursor/agent.v1.AgentService/Run, carried over Connect with content type application/connect+proto.
Sluis reads the Connect frames without a schema and applies your organisation's data-protection mode to the prompt text inside them:
- tokenize replaces detected values with reversible placeholders and restores the originals in the streamed reply.
- mask redacts them outright.
- block refuses a turn that contains detected values, before anything reaches Cursor.
- allow_log forwards the frame, and the audit trail records that it was not inspectable.
Under tokenize, mask and block, a frame Sluis cannot decode is refused with 422 instead of forwarded.
Two limits come with this transport:
- Name recognition and the prompt-injection guard read a JSON request body, which Connect protobuf is not, so neither runs. The audit row records them as not run, and if your organisation made name recognition mandatory, the turn is refused (
503) instead of forwarded unchecked. - Connect reports no token usage, so a Cursor turn is sealed into the audit trail without token counts.
Credential headers
Each ingress accepts its credential in exactly one form: x-api-key on the Claude ingress, which is what Anthropic clients send, and Authorization: Bearer on the Codex, Cursor and MCP ingresses. The same agent key in the other header is refused with 401.
MCP plugins
Governed tools arrive over one stateless endpoint, POST /agent/mcp. It keeps no session: every request re-derives the whole authorization chain, so revoking a key, a plugin or a signing key takes effect on the next call.
Two classes of plugin
- Sluis-maintained plugins are compiled Sluis code, offered organisation-wide. They run no tenant code at all.
- Organisation plugins are your own: a TOML manifest, signed with Ed25519.
How a manifest is accepted
- Its signature must verify against a signing key your organisation has enrolled.
- It is immutable per
(organisation, id, version): a changed tool definition is a new version, never a silent edit. - It is pinned to one governed HTTPS MCP server, whose endpoint must match the URL inside the signed manifest exactly.
Where a plugin applies
- Signed MCP plugins grant capabilities to one exact agent key, so they bind only at key scope.
- Context and skills are organisation policy: an owner or admin applies them to the whole organisation or to a member, never to one key.
- A signed plugin or text block bound nowhere is exposed or injected nowhere.
Server URLs, manifests, signatures and upstream credentials never reach a client. A developer sees tool names and schemas, and nothing else.
Context and skills the gateway injects
Your engineering standards are only policy if a developer cannot forget them. A CLAUDE.md committed to the repository is a suggestion: it can be edited, deleted or simply not read, and nothing records which. The same text pushed into every governed agent request from the gateway is the organisation's decision.
For example:
- Write the failing test before the fix.
- Never add a dependency without an approved ADR (architecture decision record).
- This repository holds personal data, so pseudonymize before you paste.
This is the half of the harness that governs how an agent works, rather than which model and tools it may reach. Two plugin kinds carry it, and neither grants any capability of its own:
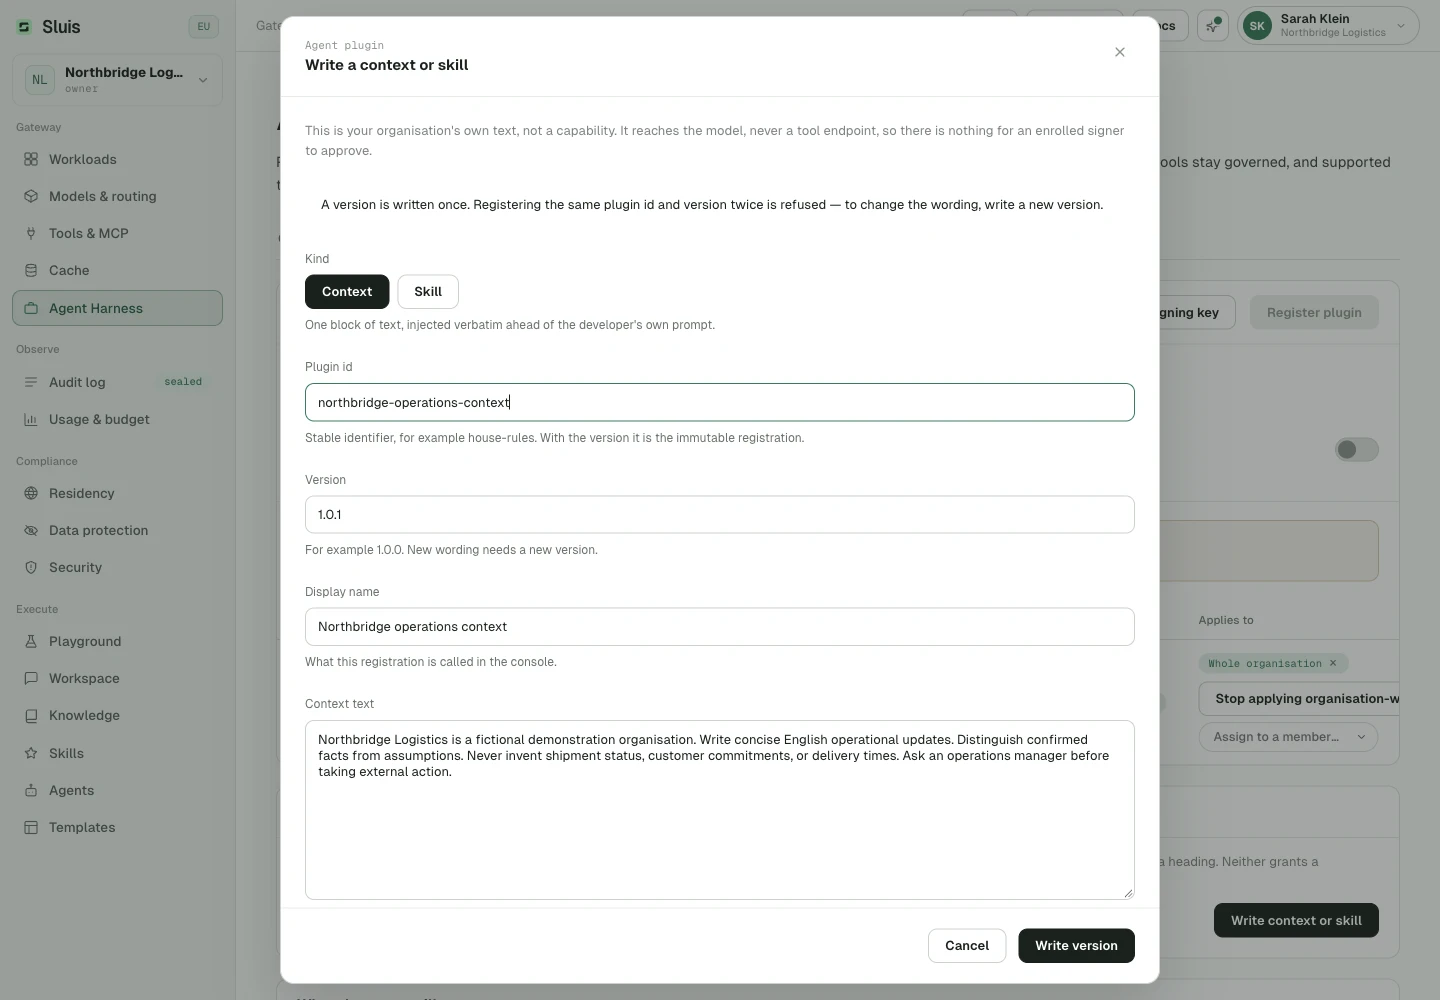
- Context. Verbatim text, injected ahead of the developer's own prompt, up to 16 KiB per version.
- Skill. A name, its instructions and the tool names it expects. Those names are intersected with the tool ceiling recorded on the key, so a skill can never widen a key: a tool the ceiling does not carry is left out of what the model is told.
Where a version applies
A version is bound to the organisation or to one member, and every request resolves both:
- Organisation. Every agent key in the organisation, including keys minted after the binding was made. Use it for a rule nobody should have to remember to attach.
- User. Every agent key one member owns, for example an onboarding brief or a stricter posture for one person.
Binding a context or skill to a single agent key is refused: only signed MCP plugins bind at key scope.
How it reaches the model
Resolution is deterministic, because injected order changes the prompt. For each request Sluis:
- Takes the union of the organisation and user bindings.
- Re-verifies each plugin exactly as it does for tools, and drops duplicate versions.
- Orders organisation first, then user, so the general rule is read first and the narrow exception last.
- Injects context verbatim and each skill as a named section.
Where the blocks land:
- On the Claude ingress they are prepended to
system, in either shape that API allows. - On the Codex ingress they go to
instructions, or in as a leading developer instruction when the request carries none.
If the plugin store cannot be read, or a version fails its integrity check, nothing is injected for it and the request still goes through. The audit row then carries no marker for that version.
Size cap
Everything injected into one request fits inside 32 KiB. Past that the request is refused with a 422 naming the plugins that overflowed the cap. Nothing is silently truncated: half an instruction is worse than none, and an organisation that believes a rule is in force has to hear when it is not.
Data protection
Injected text is not rewritten by data protection, and the order is one-way: the developer's prompt is scanned and pseudonymized first, then your policy is prepended.
These blocks are your own governed content, written in your own Console, so nobody needs protecting from them. Tokenizing would also destroy what they say: “Escalate to security@example.com before pasting” turned into “escalate to «EMAIL_1» before pasting” is no longer an instruction anyone can follow.
No signature
Context and skills are written in the Console and carry no signature. A signature stops a manifest from pointing a governed credential at an endpoint nobody approved, and a block of text points at nothing. Everything else that makes a registration trustworthy still holds:
- A version is immutable and its exact bytes are hashed.
- The row records who wrote it and when.
- A manifest carrying an MCP entry keeps the mandatory signature and the enrolled-signer check on every request.
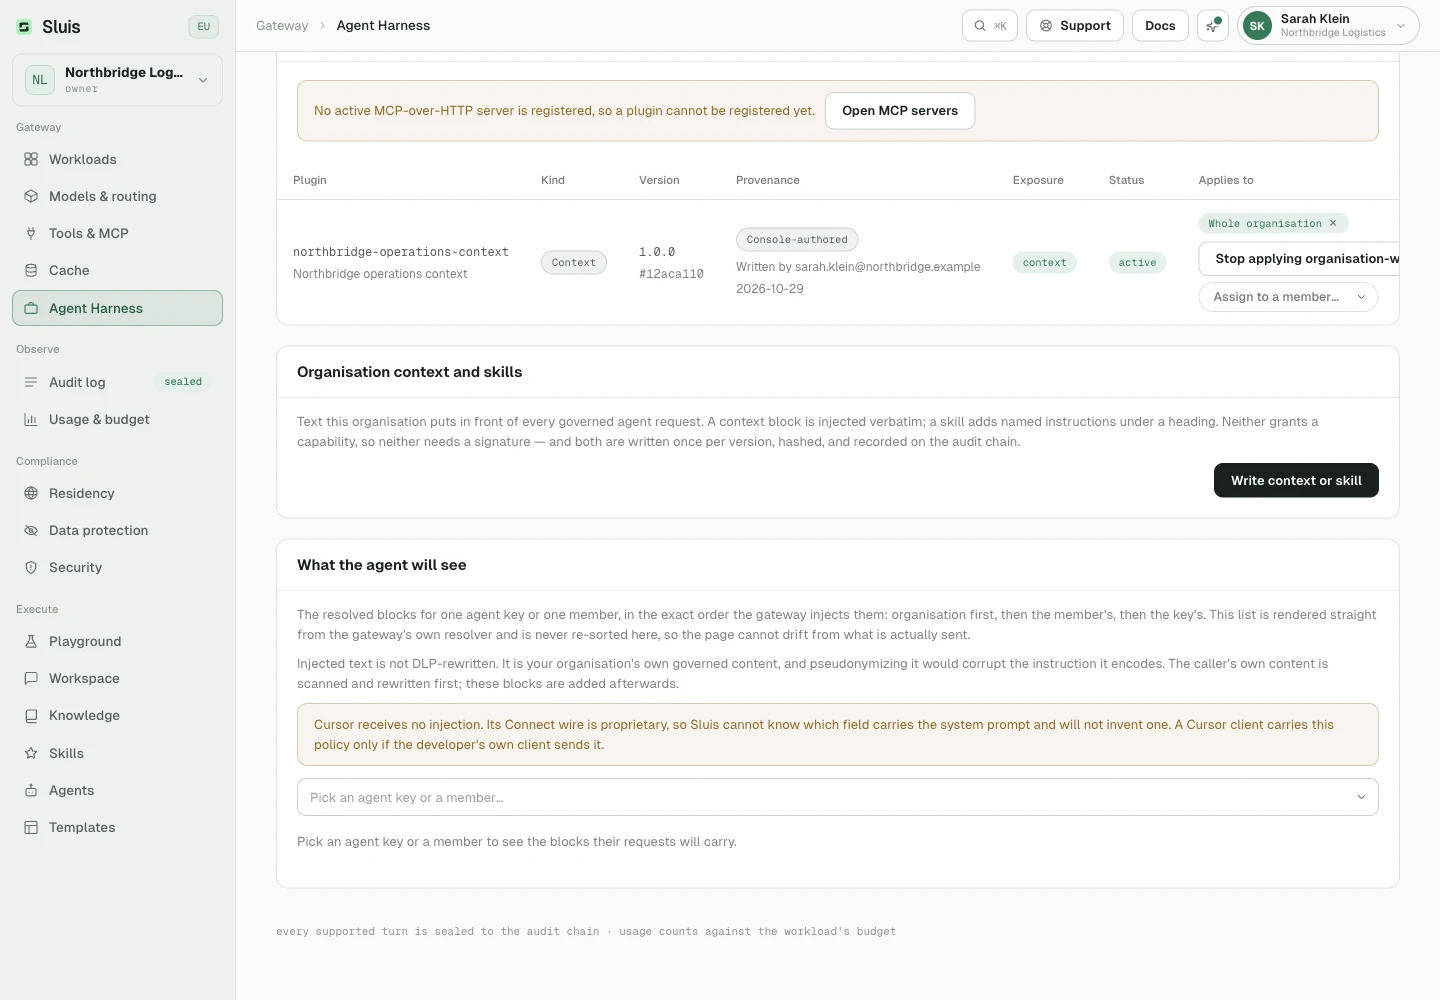
The Plugins tab shows whether a version is signed or console-authored, and previews the resolved blocks, in injection order, for a chosen key or member.
Audit marker
Each injected block leaves one marker on the sealed audit row: context:<plugin_id>@<version>#<digest8>. The digest is the first eight characters of the SHA-256 hash of that version's stored manifest.
Because a version is immutable, the marker names the exact version the model was handed, so the audit trail alone answers whether an agent was under a given rule at the moment it acted.
Cursor
Cursor is the honest gap. Its /agent/cursor transport is a proprietary binary schema: Sluis can find and rewrite the text inside those frames, which is how data protection works there, but it cannot tell which field is the system prompt. Writing into a guessed field would corrupt the request instead of governing it.
So nothing is injected on that ingress, and a Cursor turn carries your context only if the developer's own client sends it. The Console's preview says the same.
Governance that still applies
Requests from AI agents are ordinary Sluis requests, with one exception. All of this still applies:
- Data protection (DLP scanning and pseudonymization) runs before dispatch, including inside Cursor's protobuf frames.
- Agent keys stay purpose-isolated, and the harness is gated per organisation (see Availability).
- The key's rate and budget limits are enforced per request.
- MCP tools are gated call by call.
- Every model request and tool call is audited and metered, and audit rows are sealed.
The exception is residency. For model requests on the coding-agent routes the policy is recorded rather than enforced, for the reason in the note at the top of this page.
The rules are the ones described under Data protection and Budgets & caching, and they are organisation policy: an agent key cannot loosen them.
Billing
Each active Sluis-managed provider account (Claude, Codex or Cursor) costs €16.50 list price per calendar month, charged at most once per account per month. It is billed to your top-level billing root and appears as its own invoice line, separate from metered usage. VAT and the payment-method surcharge apply exactly as they do to the rest of the invoice.
Disconnecting an account stops future months. Reconnecting the same subscription reuses the existing account instead of adding a second billable one, so a disconnect and reconnect inside one month still bills once.
Gateway usage itself stays consumption-billed, exactly as for API keys.
Availability
The Agent Harness view appears in the Console once the agent_harness rollout flag is on for your organisation, which it is by default. An owner or admin can switch it off in Settings › Features. While it is off, the gateway refuses agent traffic with 404.
Troubleshooting
| Symptom | Cause and fix |
|---|---|
| 401 or 404 on an / | The key is on the wrong surface or in the wrong header. An API key on /agent/* gets a bare 404, an agent key on /v1/* or in the wrong header gets 401. Use an agent key on /agent/*, in the header form that ingress takes. |
| 502 no credential configured for provider | The agent key names a provider it has no linked account for. A key spends only the subscriptions it is linked to and never falls back to the organisation's other credentials. Link an account for that provider, or name a model the linked one serves. |
| 428 this agent key has no active Cursor account | The key has no Cursor subscription linked, or the linked one is not active. Link a Cursor subscription, or reconnect it in the Console. |
| Subscription refresh rejected | The provider refused the refresh permanently, so the account stops serving until a person reconnects it. Reconnect it in the Console: the same subscription reuses its existing account and its existing monthly fee. |
| 400 mcp_servers is not supported | A remote MCP declaration in the request is refused before dispatch, because a server reached from the model would bypass the tool gate. Register the server with Sluis and reach it over the MCP ingress instead. |
| No setup snippets in the Console | The deployment has no validated public gateway URL, so the Console shows no endpoints. Set SLUIS_GATEWAY_PUBLIC_URL to an https origin, then reload Gateway › Agent Harness › Connections. |