Skip to content

Every request.
Under your control.

Sluis Gateway puts the connection between your apps, agents and AI under one policy: a budget per workload, routing within policy, sensitive data inspected and proof of every decision. Your developers keep their SDKs and coding agents.

ISO 27001 certified

Sluis consoleIllustrative record

request / board-summarySealed

  1. Inspect2 values protected
  2. RouteEU-owned provider
  3. Seal4f9c2a…b40a
Keep your existing SDKEU-only by defaultModel and tool controlsOne audit trail

A place for every
team, app and agent.

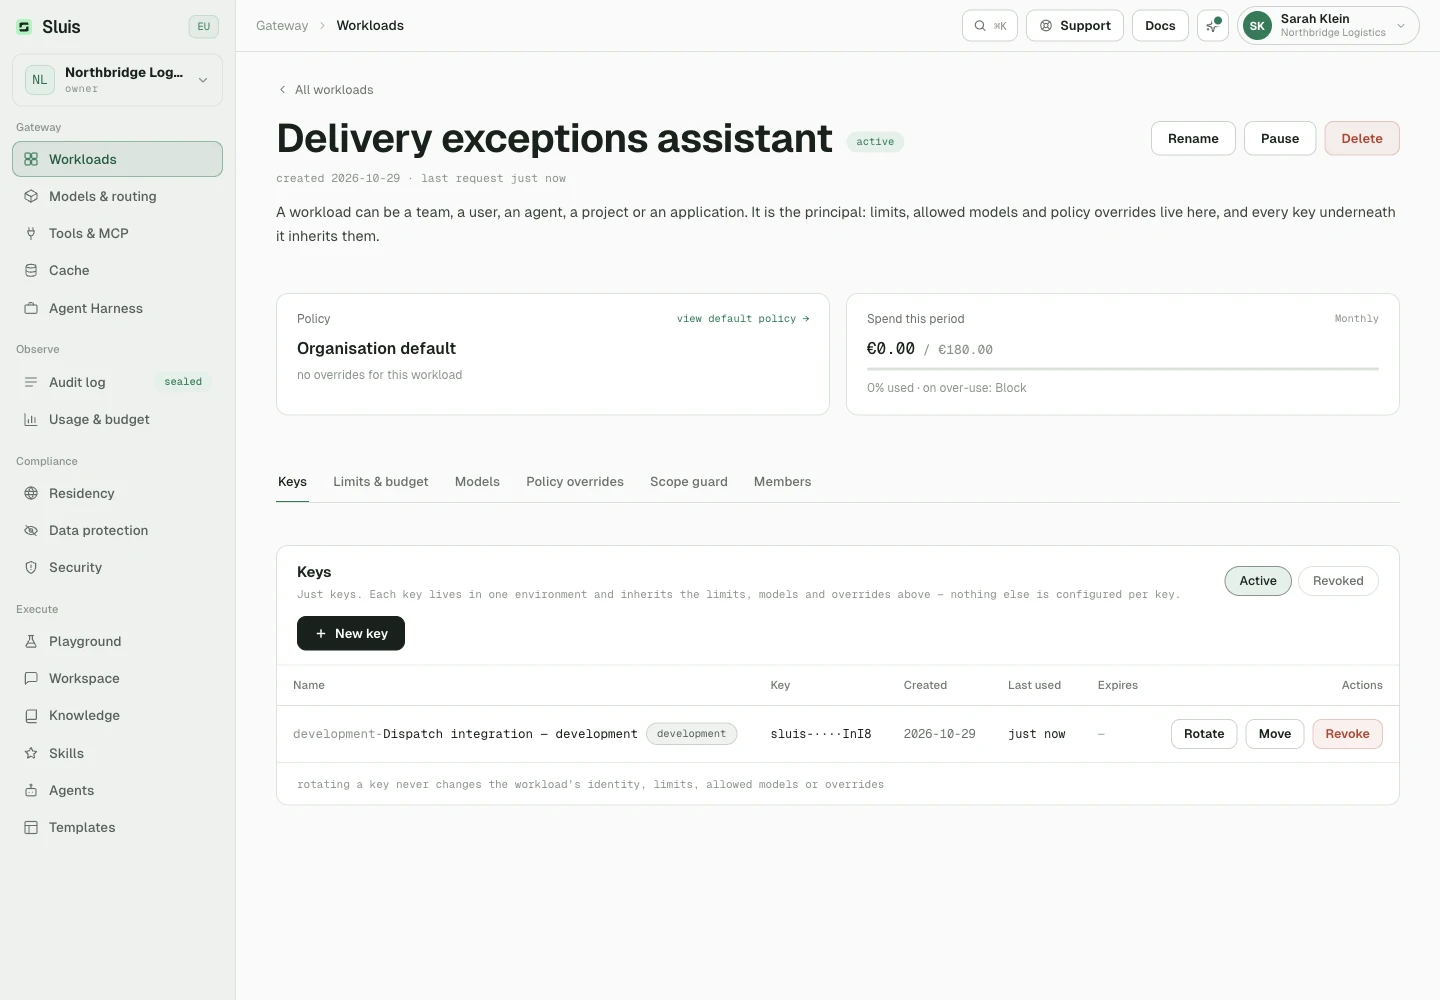
Manage AI through workloads. Each one brings its model access, budget and policy together, with a clear record of who used what.

Explore workloads
Workload credentials: manage API keys and their access settings.

English interface · illustrative demo data. Open the image for full size.

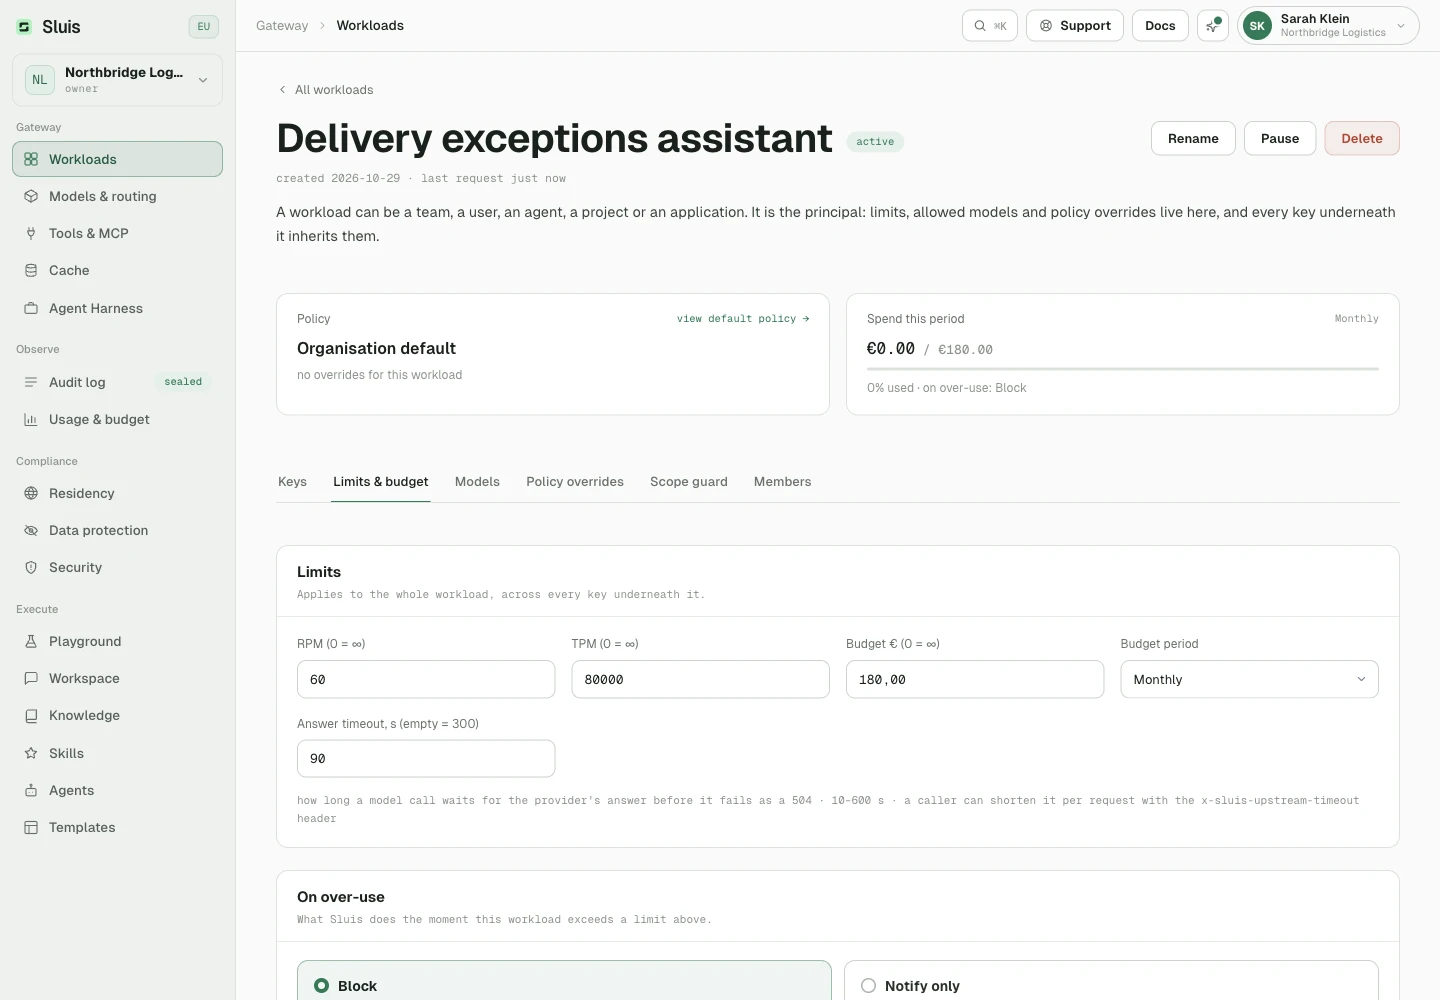
Workload limits and budget, including the provider answer timeout.

English interface · illustrative demo data. Open the image for full size.

Start with your defaults.

Every workload inherits your organisation’s policy. Overrides can tighten or loosen data protection and security; residency and provider access stay within the organisation’s allowed scope.

Decide what happens at the limit.

Set budgets and request or token rate limits, then block over-use or notify while requests continue. Choose how long a call waits for the provider’s answer: on timeout it ends as a 504 that names the cause, and a stream that has started is not cut off by it.

Hold each workload to its purpose.

Write what a workload’s AI may and may not do. A small EU-owned, EU-hosted model judges every call against that scope: Block refuses calls outside it, Log records the verdict without delaying the call. Each check is billed at the judge model’s token price.

Three gates.
One governed request.

From the first byte to the final response, your rules travel with the request.

Sluis Gateway
01

Keep the context. Replace the details.

Sluis scans for personal data and secrets before a request leaves. Detected values become stable tokens. Optional prompt-injection scanning can log or block threats before egress.

Request contentBefore egress
Inside your boundary

Prepare a payment plan for
Alex Morgan, alex@example.com

Personal data replaced
The model receives

Prepare a payment plan for
«PERSON_NAME_1», «EMAIL_1»

Original values stay inside the boundary.
Audit log: inspect sealed requests and their gate decisions.

English interface · illustrative demo data. Open the image for full size.

AI for teams with real responsibilities.

Talk about your team
Ministerie van Justitie
Omgevingsdienst de Vallei
DCMR Milieudienst Rijnmond
Omgevingsdienst Groene Metropool
Omgevingsdienst Utrecht (ODU)
Omgevingsdienst Midden-West-Brabant
RDW
Adjust
Universiteit van Amsterdam
NHA
Moco Museum
Chemgas
InShared
Het Oranje Kruis
Storteboom
Hyva
Arbeid.ai
Kleentec
Rho Adviseurs
Bezwaarschriftenadviescommissie (BAC)
SoundAware
DLV Advies
Star-shl
Stratego
Contakt
NeKo Ship Supply
Hulshoff
Logisnext / Mitsubishi Forklift Trucks
Bloem Infra
Loendersloot Group
Procap
Condor
Hoogheemraadschap van Rijnland
Aegir Marine
VO-raad & PO-raad
Weekamp Deuren
DBF
STL
Voetbal International
Sena
Move Beyond
Farmplus
Woonbedrijf
Boekenbalie
Medicinfo
Kwast Wijnkopers
Royal ZON
Verhoeven
ABN AMRO
BASF
Bayer
Eurocross
Gilead Sciences
Edelman
PXR
Avanti
Wim Hof Method
Nictiz
Nétive VMS

Protection that fits
the data you work with.

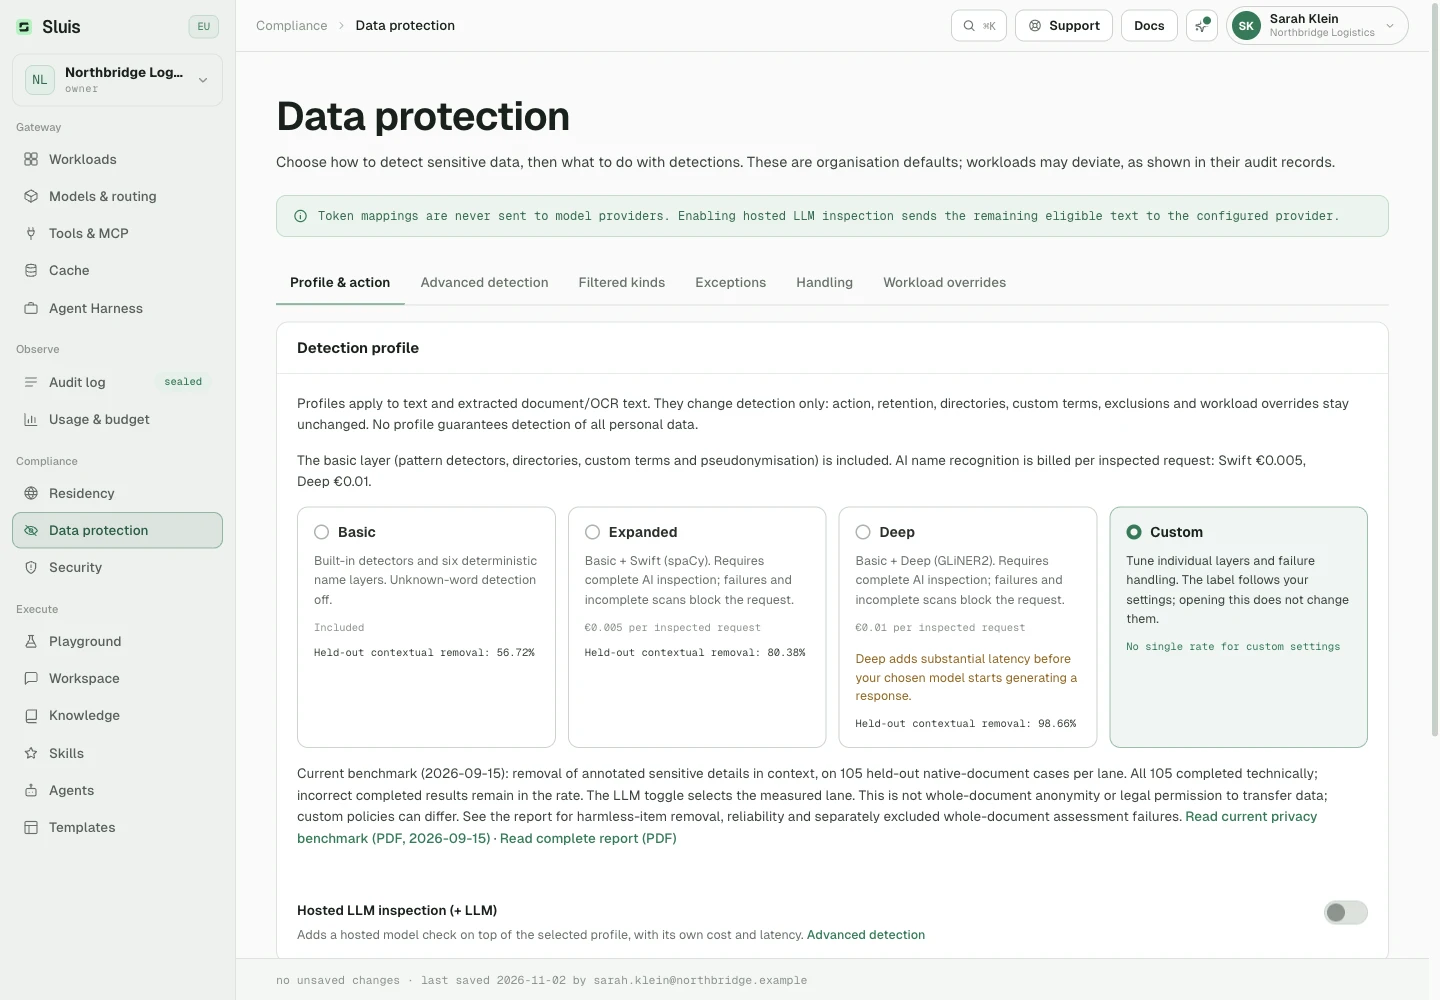
Choose a detection preset, then decide how matches are handled. Apply the same layers to prompts and extracted document or OCR text.

Data protection: configure scanning and pseudonymization.

English interface · illustrative demo data. Open the image for full size.

Choose what to detect.

Names & addressesEmail & phoneIBAN & payment detailsNational IDs & BSNAPI keys & secretsCustom terms

Detection and action are separate.

Changing a profile keeps your action, retention, directories, exclusions and workload overrides in place. No profile detects every piece of personal data.

Optional hosted LLM inspection

After local protection, an optional hosted model checks the remaining eligible text. Sluis verifies matches and tokenizes them locally. Token mappings are never sent to the provider. This option adds model cost and latency and must fit your residency policy.

EU first.
Your policy from there.

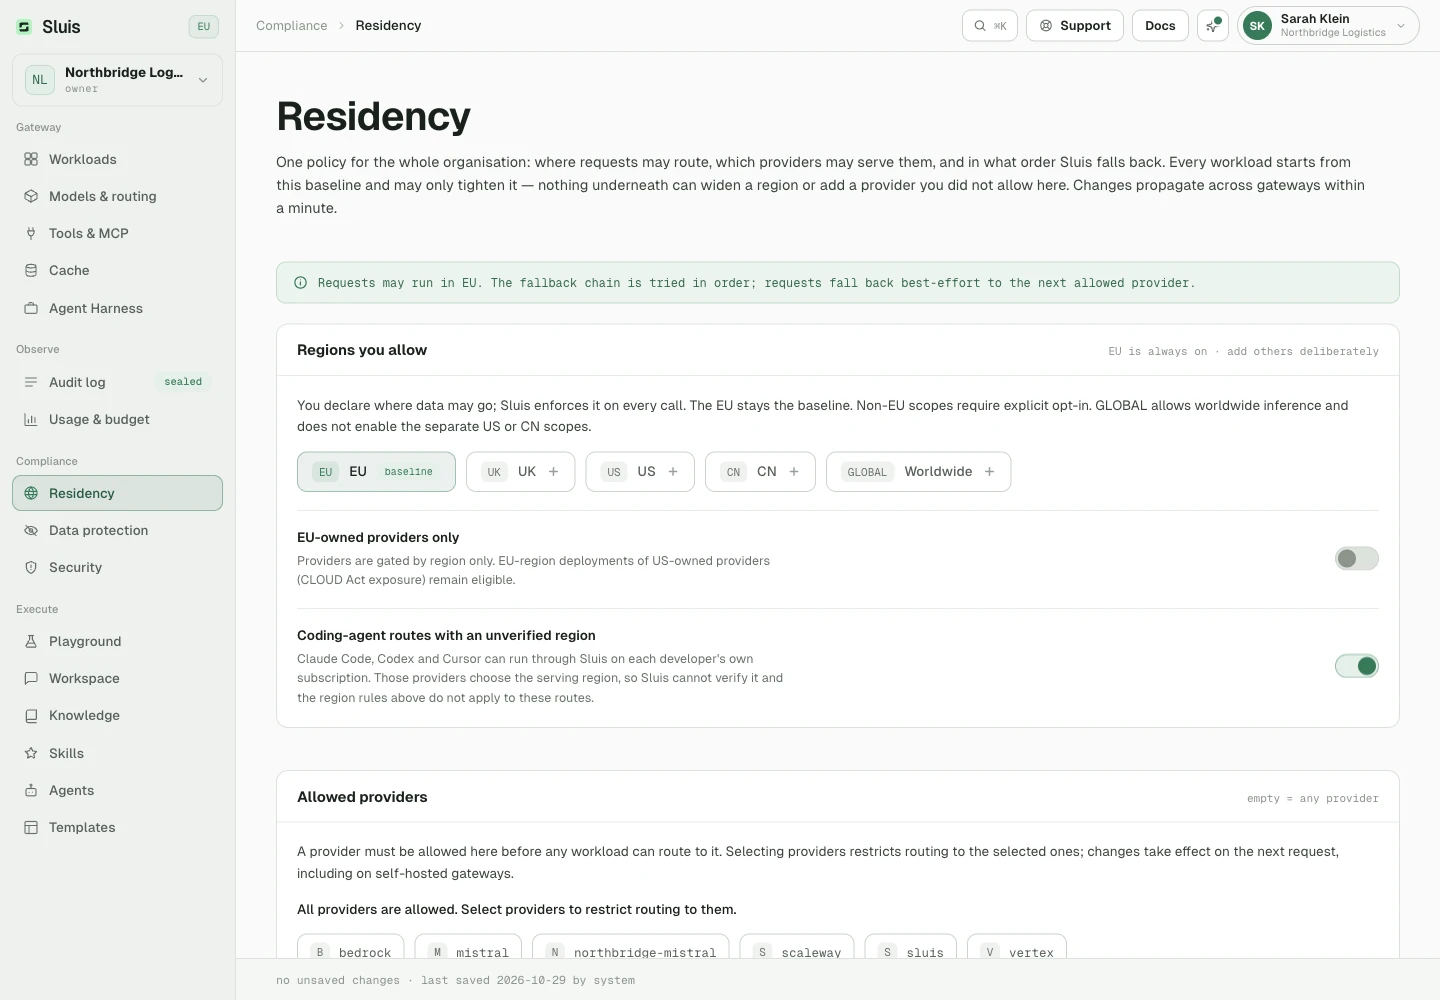
Start with a residency preset. Review the DPA against the providers your organisation can actually reach.

Explore residency & agreements
Residency: choose where requests may be served.

English interface · illustrative demo data. Open the image for full size.

A DPA for your configuration.

Review the Data Processing Agreement with an organisation-specific sub-processor annex showing reachable model providers, regions and ownership.

The right person signs.

Appoint a legal signer to review agreements and acknowledge new international transfer destinations.

A record you can refer to.

Agreement acceptances carry their version and timestamp in your organisation’s audit trail.

More choice.
A clear way to choose.

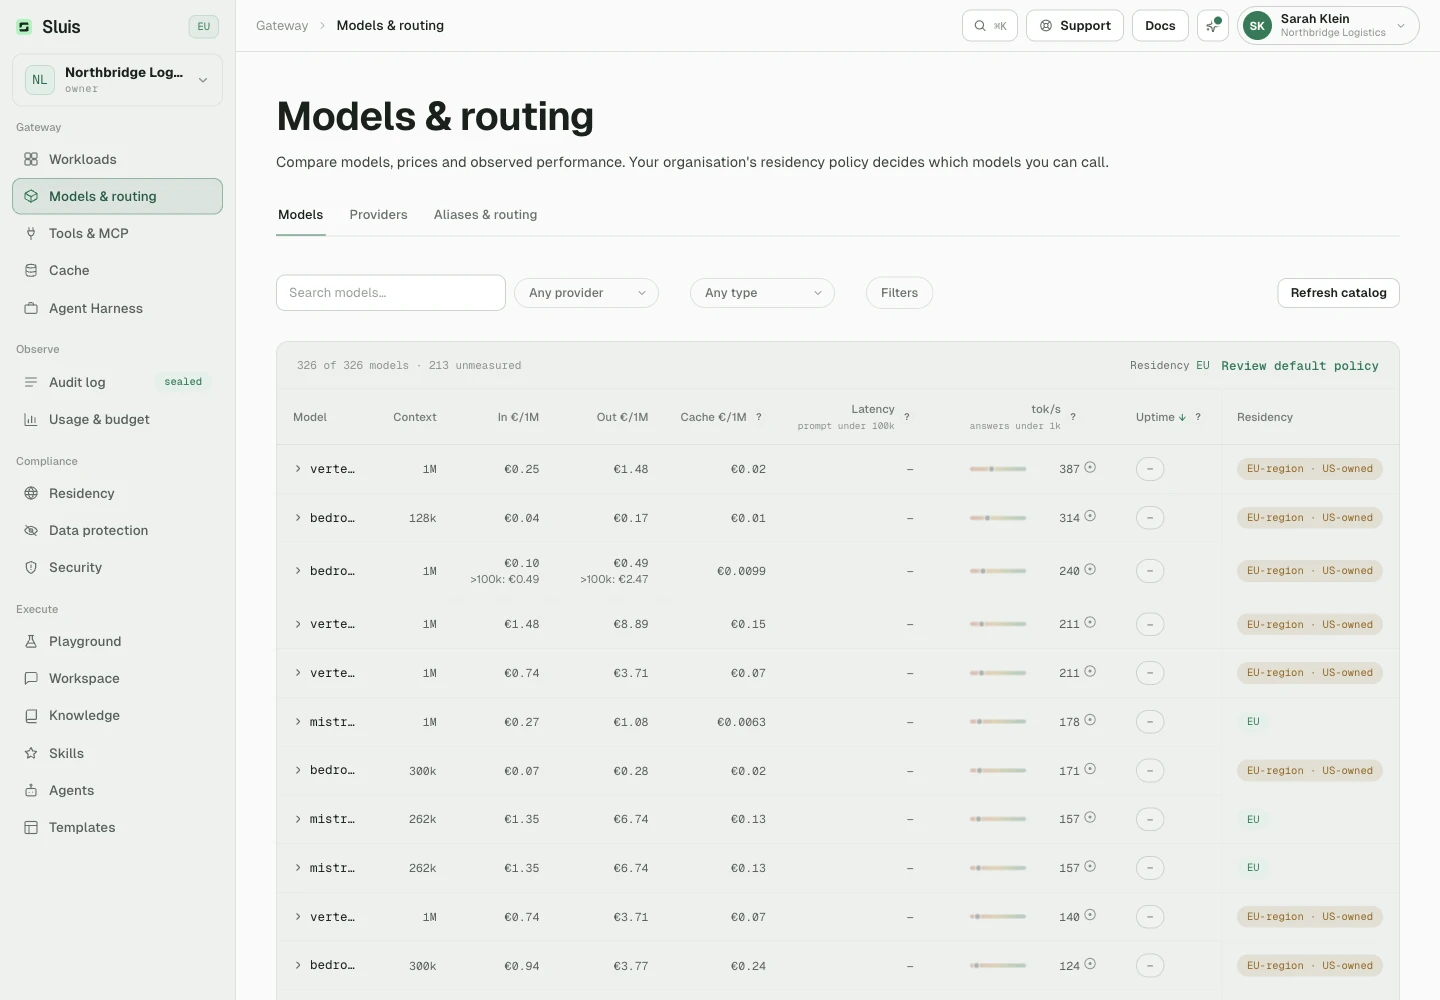
Models, providers and routing in one place. See the trade-offs, then give your applications a stable way to call AI.

Explore models & routing
Model catalog: browse available models and filter by provider and capabilities.

English interface · illustrative demo data. Open the image for full size.

Watch what comes in.
Notice what changes.

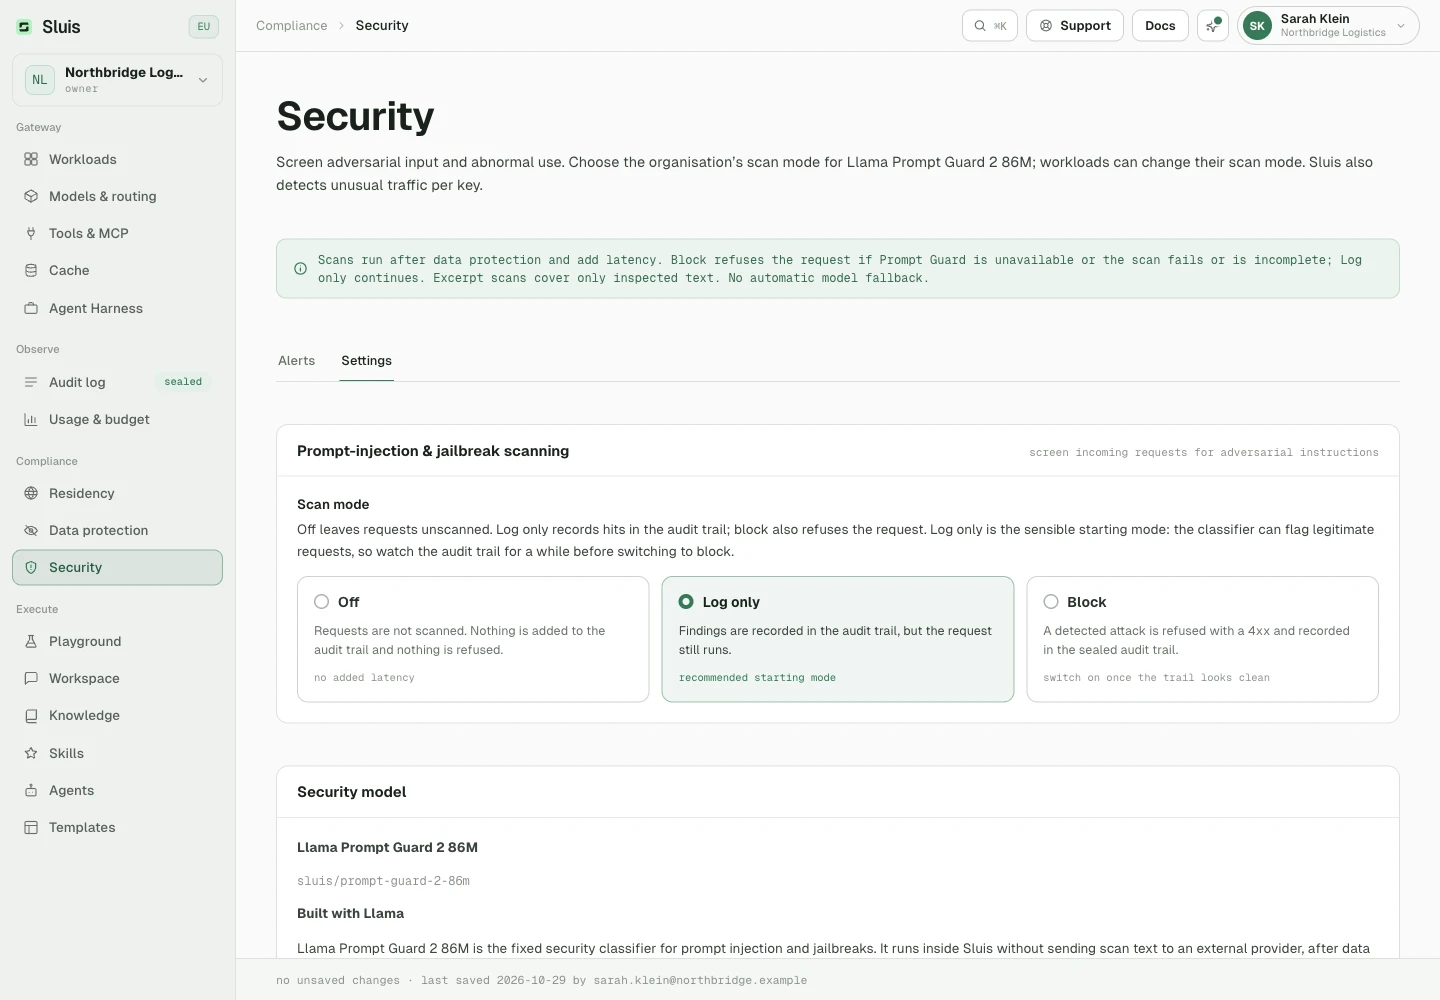
Screen for prompt injection and jailbreak attempts. Detect unusual credential activity with analysis that runs in the background.

Security: configure prompt-injection scanning.

English interface · illustrative demo data. Open the image for full size.

Choose how to respond.

Start in log-only mode, inspect the findings, then decide where to block. Set organisation defaults and adjust the scan mode for individual workloads.

Spot unusual key behaviour.

Flag changes in request volume, usage hours and model choices. Review the evidence in security alerts, with optional emails to selected team members.

How scanning works

The security classifier runs inside Sluis. Long inputs may be sampled, so attacks can be missed and legitimate prompts can be flagged. Review the measured results and scan settings in your console.

Manage the policy as code, too.

Routing, data protection and security share one versioned policy. Edit it in the console or through the API; review history and restore an earlier version.

Read the documentation

Keep your agents.
Put policy around them.

Your working tree stays local. Sluis governs the model traffic and tool calls, with purpose-isolated agent keys.

Claude CodeRunning on your machine
/agent/claude

Native agent traffic, inspected and sealed.

Agent keyIsolated
Data inspectionApplied
ToolsGoverned
Audit recordSealed

Model traffic and tools.

MCP calls pass through inspection, residency controls and the same audit chain. Tool access starts with explicit grants.

Keys with a specific purpose.

Agent keys cannot call the standard API. Provider credentials remain encrypted in Sluis.

Agent Harness is enabled per organisation as it rolls out. Coding-agent serving regions are chosen by providers and recorded as unverified.

Agent setup documentation

Sign in from your MCP client.

Point Claude Code, Codex, Cursor or another MCP client at /agent/mcp. It opens your browser, you sign in as usual and approve its access. Its calls then run under your own agent key, and you can revoke a connected client at any time.

Tools under each member’s own account.

In their Sluis Workspace settings, members connect their own accounts to tools that support sign-in. Each tool call then runs as that person, not under one shared organisation token.

Private servers wait for approval.

When you allow it, a member can propose a private MCP server. It stays inactive until an administrator approves it and chooses its tools. Your residency policy still applies.
A new endpoint.
A familiar workflow.

Compatible with the OpenAI and Anthropic APIs. Keep your SDK, prompts and streaming. Give each application a workload with its own models, limits and budget. Rotate the keys underneath it without changing its policy.

OpenAIAPI compatible
AnthropicAPI compatible
main.rs
use serde_json::json;

#[tokio::main]
async fn main() -> Result<(), Box<dyn std::error::Error>> {
    let key = std::env::var("SLUIS_KEY")?;
    let response = reqwest::Client::new()
        .post("https://api.sluis.ai/v1/chat/completions")
        .bearer_auth(key)
        .json(&json!({
            "model": "sluis/auto",
            "messages": [{
                "role": "user",
                "content": "Summarise the project plan."
            }]
        }))
        .send().await?
        .error_for_status()?;

    println!("{}", response.text().await?);
    Ok(())
}
Rust dependencies · Cargo.toml
[dependencies]
reqwest = { version = "0.13", features = ["json"] }
serde_json = "1"
tokio = { version = "1", features = ["macros", "rt-multi-thread"] }
reqwest documentation

sluis/auto resolves within your organisation’s policy. A router inside Sluis decides when a request needs reasoning; classifier excerpts only go to EU-owned providers that process in the EU.

Built for the way
you run AI.

The same controls, from an individual request to your own infrastructure.

Connect to Gateway

Documents,
protected.

Protect sensitive data in DOCX, PDF, images and text. Rendering and OCR run inside the gateway, with a sealed audit record.

Explore document protection
Customer brief.docxExample
Ready for your model

Prepare a payment plan for PERSON_1.
Send the proposal to EMAIL_1.

Personal details replaced

Spend with
boundaries.
Set budgets and rate limits per workload, across every credential. Opt-in encrypted caches remain isolated to your organisation.
Configure your workloads
Project assistantIllustrative budget
€72 / €100Within budget
Scope
This workload
Cache
Organisation only
Storage
Encrypted

Your own
perimeter.

Run the whole product on your infrastructure with Sluis Edge. The same gates and ledger, under your control.

Explore Sluis Edge
Your infrastructure
Sluis Edge
InspectRouteSeal
The data plane stays with you.

Compare before you decide

Same policy.
For the people you work with.

Give your team Sluis Workspace, the workspace built on your gateway.

Compare AI gateways for EU organisations
Explore Sluis Workspace